Governa AI · GRC platform operated by LuxGap

Your risks, your compliance, your suppliers. Finally in the same console.

Governa AI replaces spreadsheets, email chasers and consolidation meetings. Risk register, NIS2, DORA, ISO 27001 and AI Act questionnaires, third-party assessments, incidents and evidence: everything is linked, segregated per client and ready for the next audit.
  • 175 NIS2, DORA, ISO 27001 and AI Act requirements, ready to assess
  • An AI copilot that queries your data without ever seeing the database
  • Data segregated per client, hosted in the European Union
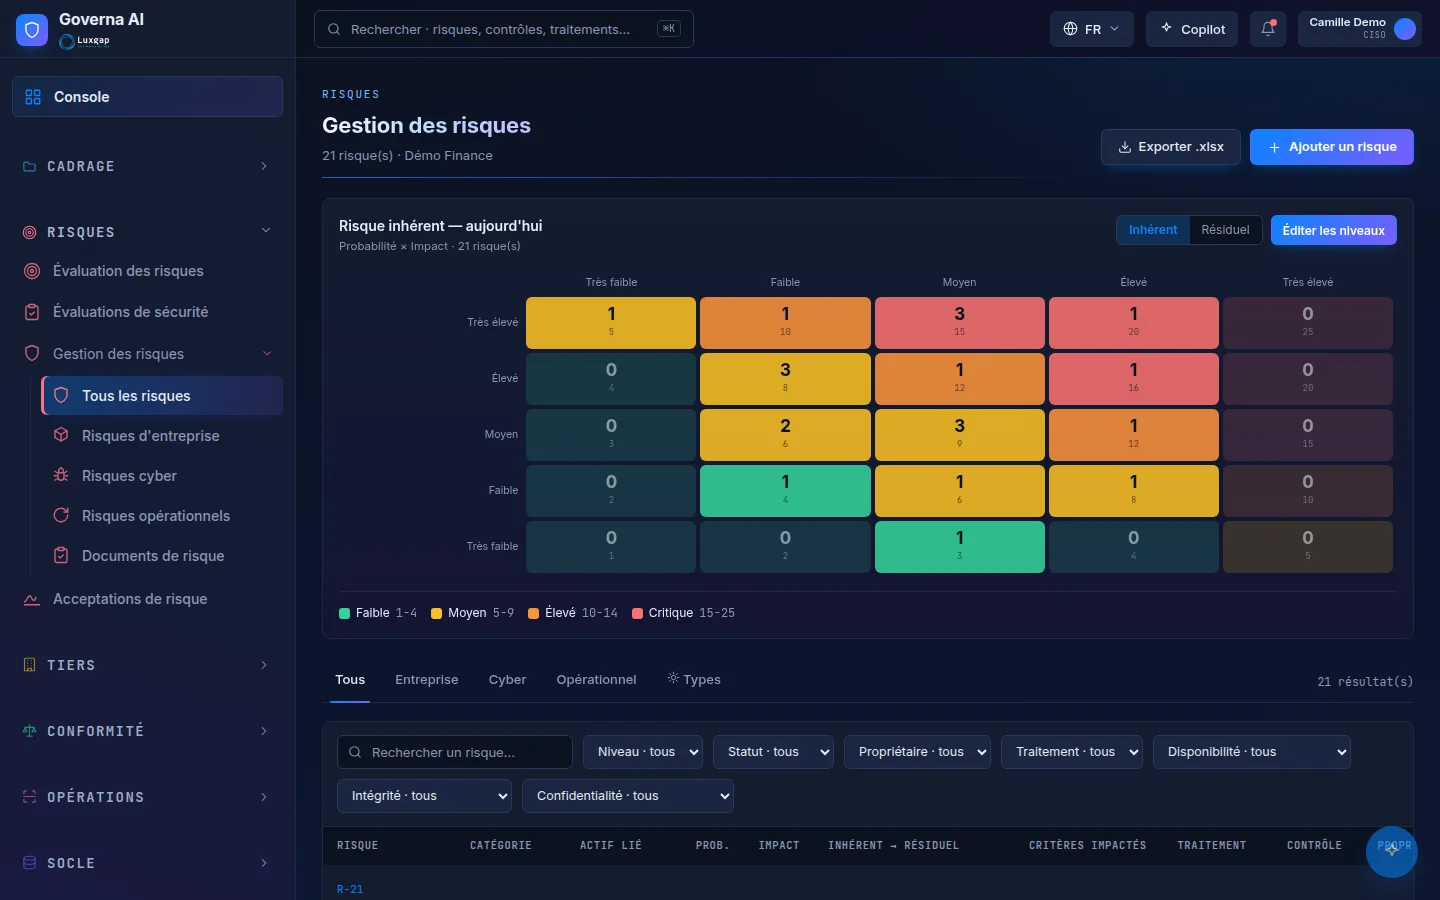
Governa AI risk register: likelihood × impact heatmap and risk list, on fictitious data
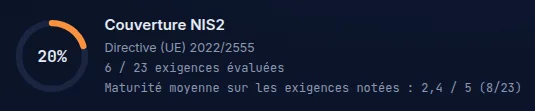
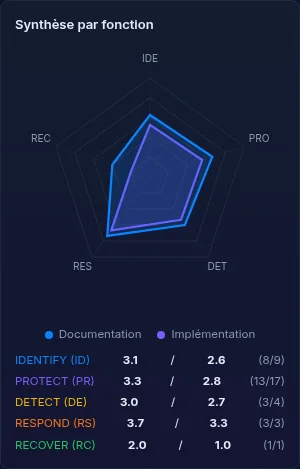
CyberFundamentals radar: documentation and implementation scores per function NIS2 coverage gauge: assessed requirements and average maturity
Screenshots of the real application · fictitious demo data

The problem

Three questions an auditor, a regulator or your board could ask tomorrow morning.

  1. Where do we stand on NIS2, requirement by requirement?

  2. Which critical suppliers have not been reassessed this year?

  3. Who accepted this risk, why, and until when?

When the answer is scattered across spreadsheets, it takes days to piece together. In Governa AI, it fits on one screen, with its source.

The platform

Seven domains, one source of truth.

Registers are linked to each other: what you enter in one place feeds the indicators, the reports and the copilot. Each client has its own strictly segregated space.

  • Scoping

    Know what you protect

    Domains, scopes, assets and actors: the map of your organisation, exportable to a spreadsheet.

  • Risks

    Assess, treat, decide

    Likelihood × impact register, ISO 27005 or EBIOS RM campaigns, justified treatment decisions and acceptances with a review date.

  • Third parties

    Stay in control of suppliers

    Weighted scoring per criterion, assessment history and concentration alerts on critical providers.

  • Compliance

    Prove it, don’t just declare it

    Guided frameworks, controls, audits, policies, due diligence questionnaires and a trust centre.

  • Operations

    Respond on time

    Incidents with notification countdowns, findings, exceptions and a calendar of deadlines.

  • Foundation

    Document and report

    Evidence register, executive dashboard, board brief and reports in PDF or DOCX.

  • Users

    Grant the right access

    Roles, a per-module permission matrix and a complete activity log, exportable to CSV.

  • Take the tour

Guided tour

What you will see from your first sign-in.

Eight screens of the real application, on a fictitious data set.

Risks

A living risk register.

  • Inherent and residual heatmap: one click on a cell filters the list.
  • Availability, integrity and confidentiality criteria on every risk (GDPR, Art. 32).
  • Justified treatment decision: owner, due date, review.

Compliance

Compliance is calculated, not declared.

  • Each requirement breaks down into three or four closed questions.
  • The status (compliant, partial, non-compliant) follows from the answers.
  • Gaps, report and remediation plan derived from your answers.

Assessments

A security assessment scored from 1 to 5.

  • Documentation and implementation scored separately, requirement by requirement.
  • Radar per function: Identify, Protect, Detect, Respond, Recover.
  • The CyberFundamentals grid or your own, imported from a spreadsheet.

Suppliers

Your suppliers, scored and monitored.

  • Weighted score per criterion, with a dated assessment history.
  • Overdue reassessments flagged: score below 70 or contract up for renewal.
  • Concentration of critical providers spotted, within the meaning of DORA (Art. 28).

Due diligence

Your clients’ questionnaires, without starting from scratch.

  • Import the questionnaire you received, as a spreadsheet, Word or PDF.
  • Governa suggests an answer to every question, with its source.
  • You review, approve, then export in the original format.

Incidents

Every notification duty has its own countdown.

  • NIS2: early warning to the ILR within 24 hours.
  • GDPR: notification to the CNPD within 72 hours.
  • DORA: major ICT-related incidents reported to the CSSF.

Analytics

Trends, not just a snapshot.

  • Risks by level over three, six or twelve months.
  • Remediation velocity: opened versus closed.
  • PDF and DOCX exports for the management committee.

Trust

A trust index your board understands.

  • A score out of 100, broken down into six weighted components.
  • Defensible strengths and weaknesses to address before a due diligence.
  • Actions ranked by score gain, trust dossier in PDF or Word.

Frameworks

175 requirements ready to assess, from day one.

LuxGap loads the frameworks into the assessment engine. You answer closed questions; Governa calculates the status, the gaps and the coverage.

  • 93 ISO/IEC 27001:2022 Annex A · security controls · 93 requirements
  • 25 ISO/IEC 27001 ISMS · clauses 4 to 10 · 25 requirements
  • 23 NIS2 Directive (EU) 2022/2555 · 23 requirements
  • 16 DORA Regulation (EU) 2022/2554 · 16 requirements
  • 18 AI Act Regulation (EU) 2024/1689 · 18 requirements

How the status is calculated

NIS2 · art. 20 Members of the management body take cybersecurity training.

  1. Have board members completed a training course? Yes
  2. Is similar training offered to employees? Yes
  3. Is attendance recorded? Partly

Calculated status Partial

All “Yes”: compliant. All “No”: non-compliant. Otherwise: partial.

AI Copilot

Ask the question. The answer comes from your data, and nowhere else.

The Governa copilot has no access to the database. It uses read-only server tools, limited to the active client: it calls them, reads their results and answers with links to the records concerned.

  1. Your question “Which critical risks are still open?”
  2. The copilot AI model operated by LuxGap.
  3. Seven server tools Read-only, client set by the server.
  4. The answer Clickable records and suggested actions.

The safeguards

  • No direct database access: read-only server tools only.
  • The active client is set by the server, never by the content of the question.
  • At most four turns and six tool calls per question.
  • Without an AI provider, a local calculation engine takes over.
  • A technical log that never stores the conversation.

Security

Built for the data you entrust to no one.

Governa AI applies to its own data the standard LuxGap applies in its external CISO engagements.

  • Per-client segregation

    Every register belongs to a client and every read goes through segregated access. An automated test checks it on every release.

  • Roles and permission matrix

    Admin, CISO, user and your own roles: nine modules, four levels, enforced server-side.

  • Nothing is written without a grant

    A user can view. They only edit a module when their CISO explicitly grants it.

  • Complete activity log

    Every write is recorded with its before and after values, as are sign-ins and downloads. CSV export.

  • Monitored by the LuxGap SOC

    Security events are collected by the LuxGap SIEM and kept for six months.

  • Baseline protections, everywhere

    Lockout after five failed sign-ins, an anti-CSRF token on every action, security headers.

Who is behind it
One Luxembourg group, three trades.

  • Security, data protection and compliance. Publishes and operates Governa AI.
  • Infrastructure and server operations.
  • Development of the platform software.

  • European hosting Application and data hosted in the European Union.
  • Luxembourg authorities Notification deadlines aligned with the ILR, the CNPD and the CSSF.
  • Human support LuxGap’s external CISOs and DPOs can run the platform with you.

Onboarding

Four steps, supported by LuxGap.

  1. Scoping

    Your domains, scopes, assets and priority framework.

  2. Configuration

    Roles, permission matrix, likelihood and impact scales.

  3. Migration

    Import of your policies, your assessments and the questionnaires you receive.

  4. Support

    Hand-over to your teams, backed by LuxGap’s external CISO if you wish.

FAQ

Frequently asked questions.

For anything else, the demo is the right time to talk about it.

Book a demo
Who is Governa AI for?

CISOs, DPOs and compliance managers of organisations subject to NIS2 or DORA, or working towards ISO 27001, and the LuxGap teams that support them. Each organisation has its own strictly segregated space.

Which frameworks are available?

ISO/IEC 27001:2022 (Annex A and ISMS), NIS2, DORA and the AI Act, 175 requirements in total, plus scored security assessments such as CyberFundamentals. The engine is data-driven: adding a framework means loading its content.

Does the AI see our data?

The copilot never accesses the database. It calls read-only server tools, limited to the active client, and only receives their results. Without an AI provider, answers are calculated locally.

Where is our data hosted?

In the European Union, on the infrastructure run by LuxOps for the LuxGap group. Each client’s data is segregated and every action is logged.

Can we get our data back?

Yes: registers in XLSX, the activity log in CSV, reports and dossiers in DOCX or PDF.

Is the interface available in English?

Yes, the interface is available in French and English. The copilot currently answers in French.

How do we get started?

Book a demo: we walk through your risks, your priority framework and your critical suppliers together, then we open your space.

See Governa AI on your own challenges.

A walkthrough of the platform, a conversation about your obligations and a proposal tailored to your organisation.